Ariel Millennium Thornton @arielmt@computerfairi.es
- Pronouns
- she
- Species
- feline/phoenix (shifts at will between them)
- Fairy wand currently on
- GEOS programming guide
- Website
- https://thornton2.com/ArielMT
Admin
✨ Kind 'Net Help Desk fairy by day. ✨
✨ Weird & furry Unix fairy by night. ✨
✨ Sometimes a retrocomputer fairy. ✨
✨ Pays the ComputerFairi.es bills. ✨
✨ Sparkly✨shellscript✨princess. ✨
✨ Age: Mere days younger than ✨
✨ the Intel 4004 & Unix 1st Edition. ✨
✨ Follow requests welcome. ✨
✨ 
 ✨
✨ Move purposefully and fix things. ✨
Joined May 2017
Pinned post
Welcome to Computer Fairies, where the ✨sparkles✨ are lively fairy dust, not lifeless AI slop.
Pinned post
Don't blindly believe everything you read online, tempting as that is. Do your homework first. This video series will help you do it well: https://www.youtube.com/playlist?list=PL8dPuuaLjXtN07XYqqWSKpPrtNDiCHTzU
Pinned post
Remember to pop your filter bubble every so often. If you think you're not in one, you're trapped in one and in for a rude awakening.
Ariel Millennium Thornton
boosted
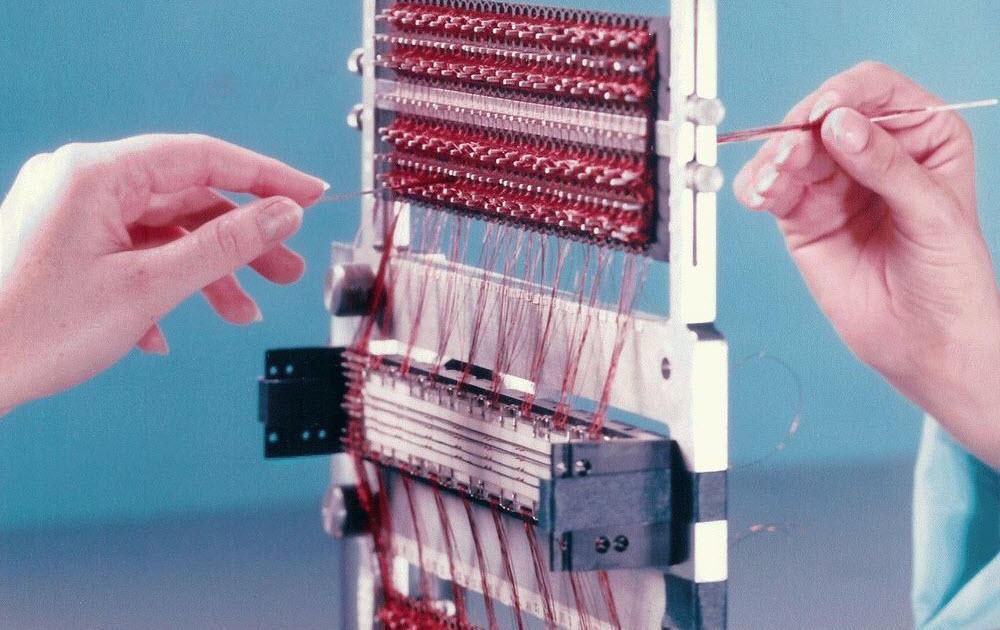
What about if we taught Sam Altman to simply weave his own memory?
re: Spam of the day
I'm pretty sure the Mariners aren't that desperate to end their status as MLB's only team without a pennant.
Spam of the day
An "Account Executive" with the Seattle Mariners wants my company to advertise at T-Mobile Park & sponsor the Mariners to help us get more business.
We're a small business with only one office, in rural New Mexico.
Yeah, this a legit offer we should definitely take up. :V
Ariel Millennium Thornton
boosted

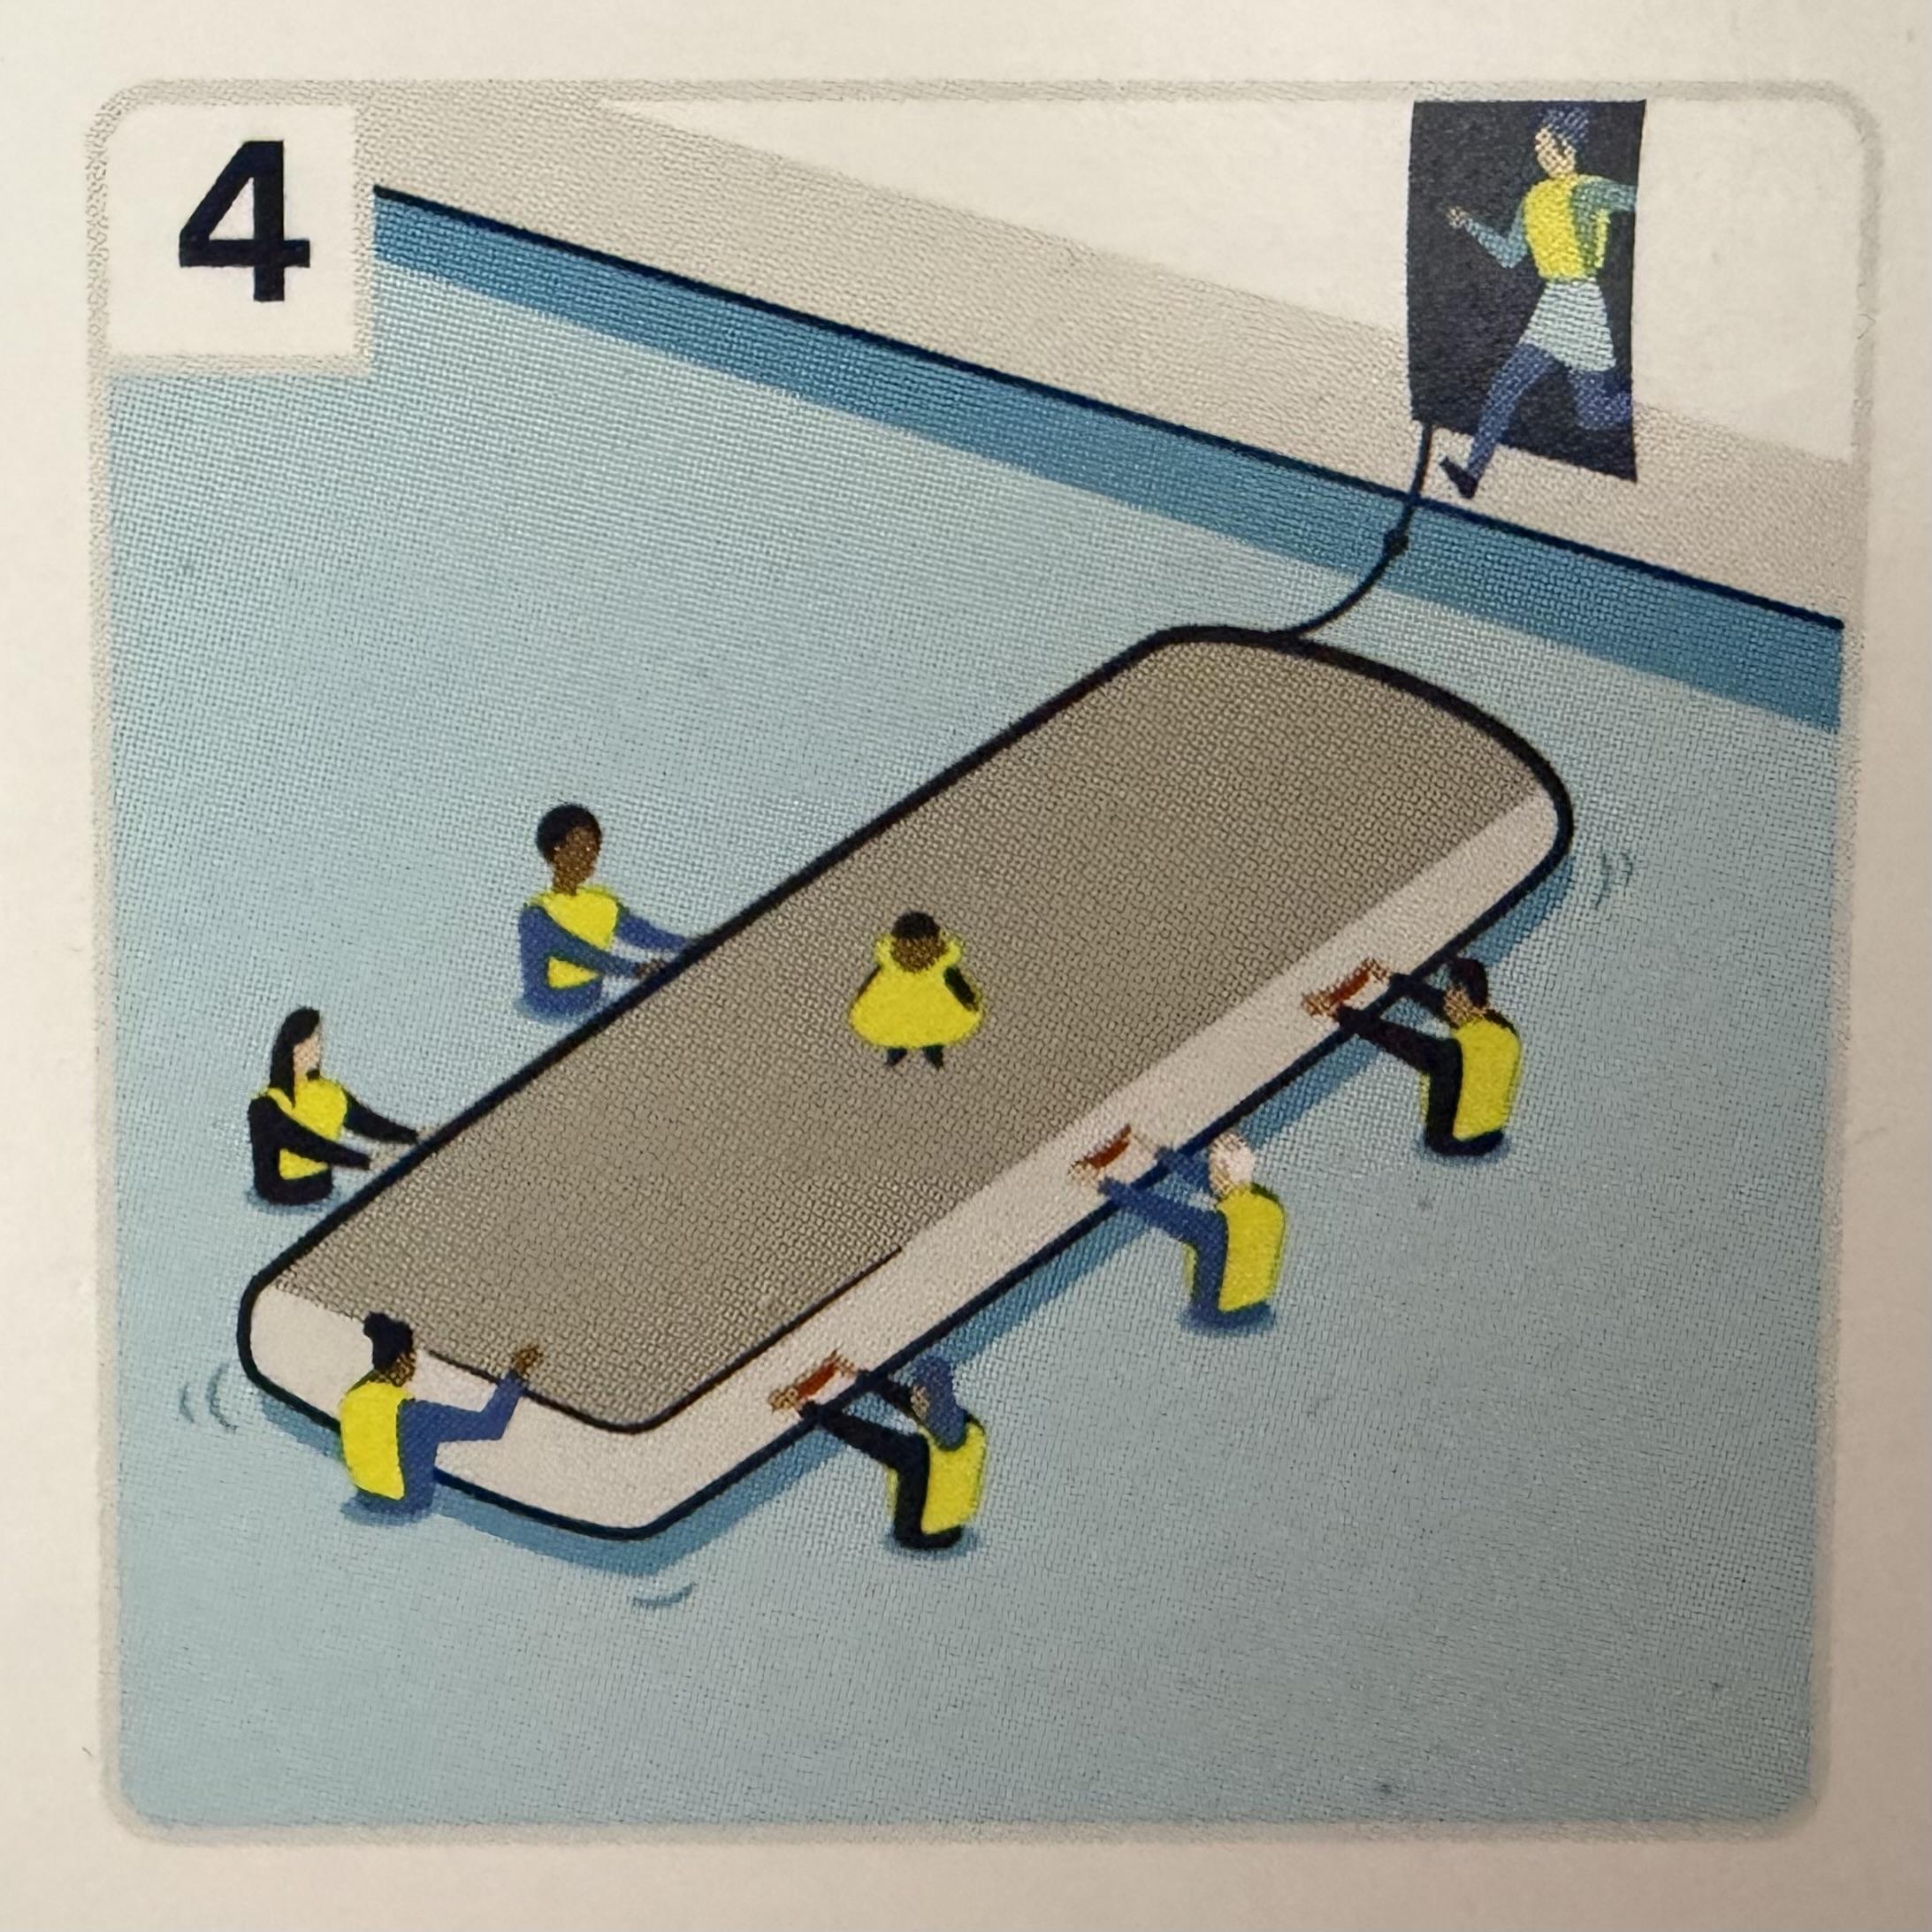
I love this panel of the 737-900 safety pamphlet, which demonstrates proper procedure for how survivors should pledge fealty to
~T h e B u o y a n t C h i l d~
Ariel Millennium Thornton
boosted

what's your plan for when AI collapses and you have to explain the years you spent forgetting how to program on purpose
Ariel Millennium Thornton
boosted
Ariel Millennium Thornton
boosted

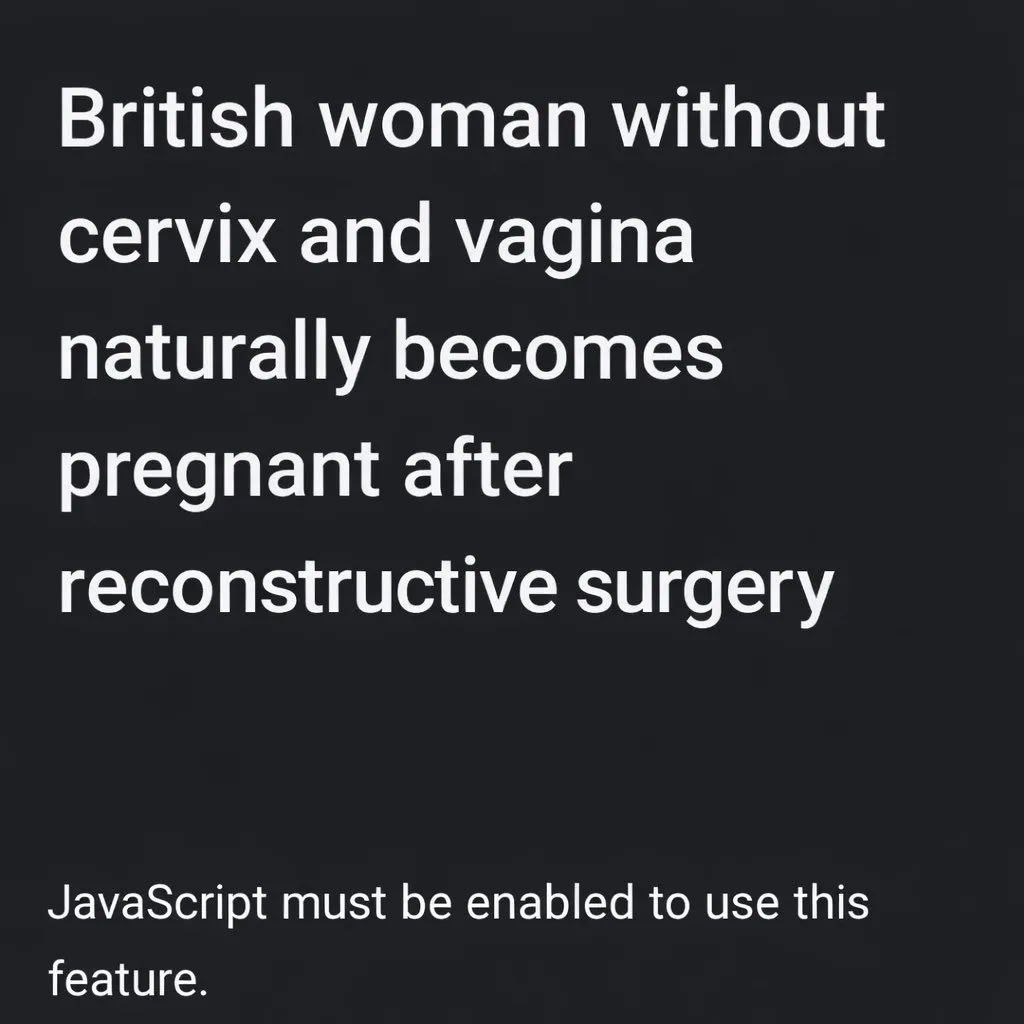
Hey, sisters, how can I install JavaScript engine in my body? 😂
Something went wrong. Refresh or try again later. $BEGIN_LINKLearn more$END_LINK
LB: Charat Yoco is also what I used to create my current av, but I edited it with some transparency blurring and overlay on a trans pride flag background using ImageMagick incantations I can never remember.
Charat Yoco: https://charat.me/en/profile/
Ariel Millennium Thornton
boosted

I found the character creator app again that I used to create my famous profile avatar in 2018: https://charat.me/en/profile/ (runs completely in the browser)
Ariel Millennium Thornton
boosted
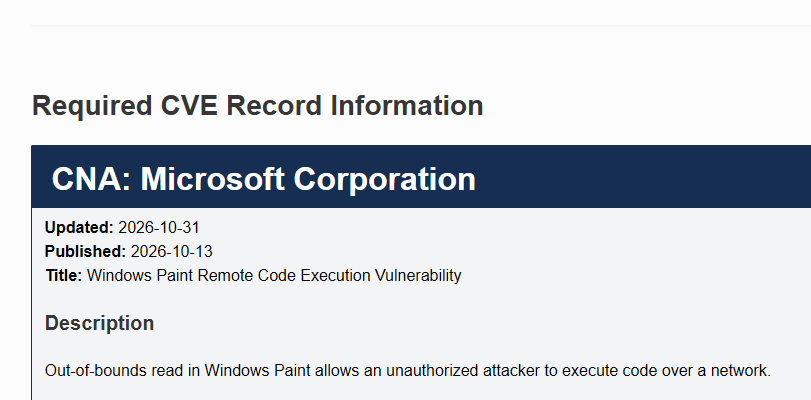
WHY IS MS PAINT *CONNECTED TO THE INTERNET*
WHAT THE FUCK
Ariel Millennium Thornton
boosted

Ariel Millennium Thornton
boosted

none pam with left musl
Ariel Millennium Thornton
boosted

Ariel Millennium Thornton
boosted
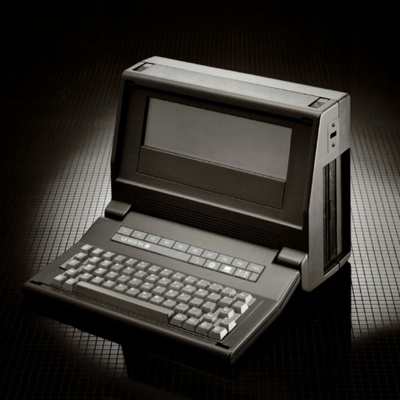
In 1985, "Computer Chronicles" covered The WELL, an early online service founded by Stewart Brand and Larry Brilliant. In 1999, Salon.com acquired what remained of The WELL. Salon's founders were WELL members who developed their initial business plan in a private forum on the service.
Today, Salon shut down. But The WELL (well.com) endures. Salon sold the service to a group of longtime members in the 2010s.
Ariel Millennium Thornton
boosted

Ariel Millennium Thornton
boosted


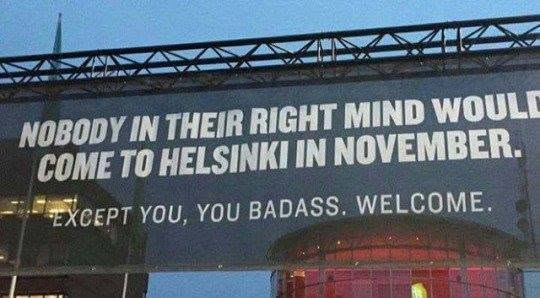
Vorbis Bueller's Day Ogg
uspol boost
RE: https://mastodon.social/@carstenfranke/117559201273902159
Boosted is a reminder that people voted, land didn't.
Ariel Millennium Thornton
boosted
OpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
https://openssh.com/releasenotes.html#10.6p2
If you operate a Linux system that uses musl libc without PAM (Alpine Linux is one example) then stop reading and set PasswordAuthentication=no or disable SSH for these systems IMMEDIATELY.
This vulnerability does not exist on non-Linux systems, Linux/glibc systems and Linux systems that use PAM for password authentication.
We consider the root cause of this bug to be outside OpenSSH itself, but we're in a good position to deliver a mitigation quickly.
We are making this release as fast as possible (we learned of the problem yesterday) because we have recently observed multiple cases of rapid bug rediscovery by AI agents, sometimes within hours, and so now consider long embargo periods to be a dangerous practice that primarily benefits attackers.
Thanks for Özgün Kültekin of Wakefield (wakefield.co) for reporting this problem to us and for the Alpine Linux developers for making an updated release available at very short notice.
Docker, Alpine Linux, and musl are in computer security news today because there's a vulnerability exploitable via SSH in one very specific but somewhat common server configuration.
- Pronouns
- she
- Species
- feline/phoenix (shifts at will between them)
- Fairy wand currently on
- GEOS programming guide
- Website
- https://thornton2.com/ArielMT
Admin
✨ Kind 'Net Help Desk fairy by day. ✨
✨ Weird & furry Unix fairy by night. ✨
✨ Sometimes a retrocomputer fairy. ✨
✨ Pays the ComputerFairi.es bills. ✨
✨ Sparkly✨shellscript✨princess. ✨
✨ Age: Mere days younger than ✨
✨ the Intel 4004 & Unix 1st Edition. ✨
✨ Follow requests welcome. ✨
✨ ✨
✨ Move purposefully and fix things. ✨
Joined May 2017